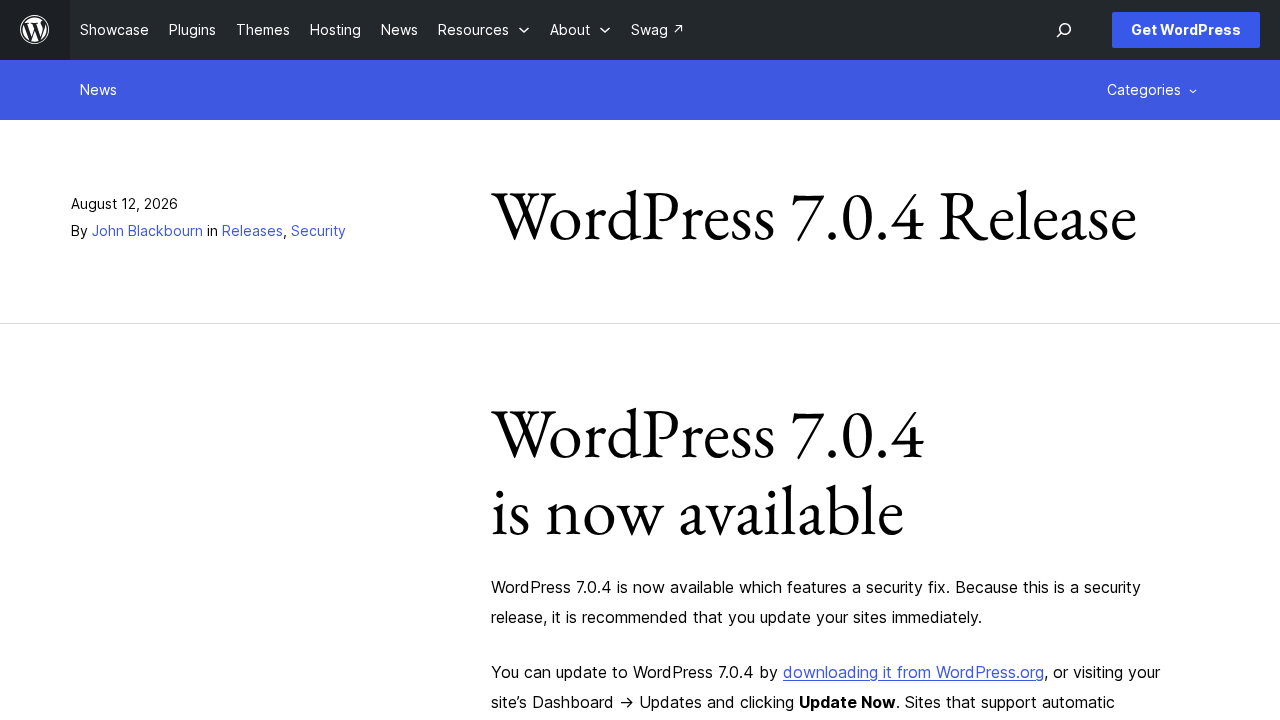
WordPress 7.0.4 was released on August 12, 2026. It is a security release with one fix, and the recommendation is to update your sites immediately.
The security fix
According to the official announcement, 7.0.4 fixes an authenticated remote code execution issue. A user with the author role or higher could upload a malicious file on sites that use Imagick and Ghostscript. Details are in advisory CVE-2026-65640.
The fix was backported to the 4.7 branch and later, and was also included in WordPress 7.1 RC3.
How to update
Sites that support automatic background updates receive it on their own. You can also go to Dashboard, then Updates, and click Update Now.
Imagick, Ghostscript and author access after WordPress 7.0.4
Whether your site is exposed depends on your server. Imagick and Ghostscript are common on hosting that processes images and PDFs. If your site gives author level access to people outside your core team, such as guest writers or members, treat this update as urgent.
Beyond the update, this is a good time to review who has author access and remove accounts that no longer need it. Fewer accounts with upload rights means a smaller attack surface.
Authenticated remote code execution with Imagick and Ghostscript (CVE-2026-65640). On sites we manage, we first check whether the server has Imagick and Ghostscript installed, since that tells us how exposed the site is. Either way, we apply 7.0.4 as soon as possible, then upload a few images and a PDF on staging to confirm thumbnails and previews still generate. If a site has no need for PDF previews, we can work with the host to remove Ghostscript, which takes away one of the conditions this issue depends on.
Want WordPress 7.0.4 and every release after it handled for you? Our support and maintenance plans cover tested core, theme and plugin updates, uptime monitoring and help when something breaks. Questions about your site? Contact us and we will take a look.